Wireshark All The Things
2026-11-18 · http
1. traceroute and ICMP packet analysis
Packet Capture Here
sudo pacman -Syu traceroute # install traceroute
The ICMP Protocol
Echo or Echo Reply Message:
    0                   1                   2                   3
    0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
   |     Type      |     Code      |          Checksum             |
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
   |           Identifier          |        Sequence Number        |
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
   |     Data ...
   +-+-+-+-+-
- Types:
8: echo request0: echo reply
Time Exceeded Message:
    0                   1                   2                   3
    0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
   |     Type      |     Code      |          Checksum             |
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
   |                             unused                            |
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
   |      Internet Header + 64 bits of Original Data Datagram      |
   +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
It is interesting to note that ICMP is a network layer protocol and mainly used by network devices to talk to each other
Traceroute
❯ traceroute -I  www.google.com
traceroute to www.google.com (142.251.223.4), 30 hops max, 60 byte packets
 1  10.145.0.3    2.861 ms  2.848 ms  2.840 ms
 2  10.120.0.25   2.833 ms  3.870 ms  3.864 ms
 3  10.250.1.9    3.856 ms  3.851 ms  3.845 ms
 4  * * *
 5  * * *
 6  * * *
 7  * * *
 8  * * *
 9  * 142.250.172.80               121.647 ms  121.600 ms
10  142.251.76.31      119.703 ms  121.583 ms  121.669 ms
11  192.178.110.244    121.572 ms  121.567 ms  119.482 ms
12  142.250.213.171    119.441 ms  119.434 ms  117.319 ms
13  216.239.49.130     117.327 ms  117.320 ms  117.314 ms
14  142.250.62.67      117.307 ms  115.186 ms  104.474 ms
15  * * *
16  * * *
17  * * *
18  * * *
19  * * *
20  lcmaaa-ao-in-f4.1e100.net   101.133 ms  103.220 ms  101.638 ms
The IPs from 9 to 14 all belong to Mountain View, California
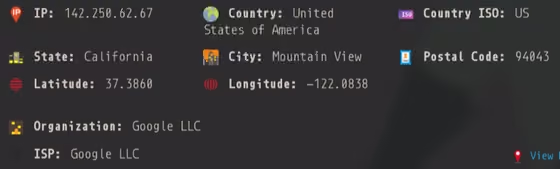
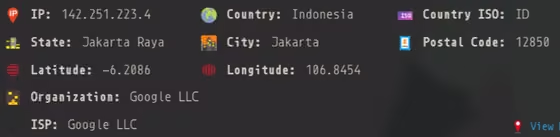
The final IP is from Jakarta, Indonesia
mtr is a similar service that combines the functionality of traceroute and ping into a single netwrok diagnostic tool it prints running statistics about each intermediate router
                     My traceroute  [v0.96]
tars (10.145.110.139) -> google.com (142.250.207.78)
                           Packets               Pings
 Host                    Loss%   Snt   Last   Avg  Best  Wrst StDev
 1. 10.145.0.3            0.0%   127    1.8  12.4   1.3 110.0  18.9
 2. 10.120.0.25           0.0%   127   27.9  15.1   1.6  86.8  21.0
 3. 10.250.1.9            0.0%   127    2.1  16.4   1.7  98.2  19.7
 4. (waiting for reply)
 5. (waiting for reply)
 6. (waiting for reply)
 7. (waiting for reply)
 8. 10.152.7.214          0.0%   127   59.0  69.2  33.8 174.0  20.4
 9. 142.250.172.80        0.0%   127   64.7  65.5  32.1 263.1  25.0
10. 142.251.76.31         0.0%   127   64.1  67.3  32.6 190.3  21.0
11. 192.178.110.244       0.0%   127   65.4  70.3  34.6 219.0  23.7
12. 142.250.213.171       0.0%   127   64.6  65.4  33.3 189.8  22.1
13. 216.239.49.130        0.0%   126   65.3  77.2  48.1 324.3  34.9
14. 142.251.229.251       0.0%   126   75.6  79.8  49.6 261.2  34.3
15. 142.251.55.207        0.0%   126  112.9  80.8  47.9 237.5  30.1
16. 142.250.207.78        0.0%   126   50.6  77.8  50.5 208.8  26.8
only just slightly different from the traceroute output :)
Control Plane Policing and Asymmetric Routing
in the traceroute and the mtr you may have noticed that the time for the final hop is significantly less than the time for some of the intermediate hops
11  192.178.110.244  121.572 ms  121.567 ms  119.482 ms
12  142.250.213.171  119.441 ms  119.434 ms  117.319 ms
where latency is 120ms
20 lcmaaa-ao-in-f4.1e100.net 101.133 ms 103.220 ms 101.638 ms
and here the latency is 101ms
The reason is that routers have a Control Plane that handles when it needs to send an icmp response back to the source. Network Operators set arbitrary rate limits on the Control Plane, that delay when a process is finally processed by the router and sent back. Whereas the final node is probably going to be configured to send a response back as soon as possible
There is also the issue of asymmetric routing where the path back from the remote machine to you may not be the same. This backward path may take longer than the forward path, introducing more delays (its usually just because of control plane policing though)
Wireshark Analysis
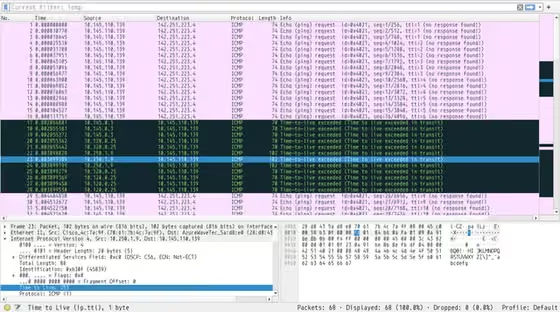
The First ICMP Echo Request
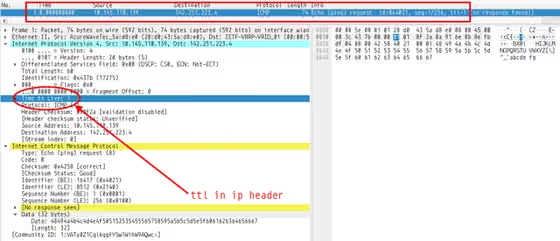
From the RFC
Time to Live
   Time to live in seconds; as this field is decremented at each
   machine in which the datagram is processed, the value in this
   field should be at least as great as the number of gateways which
   this datagram will traverse.
So the TTL is essentially set to the number of machines the packet will be routed through before hopefully being sent back to the source (me).
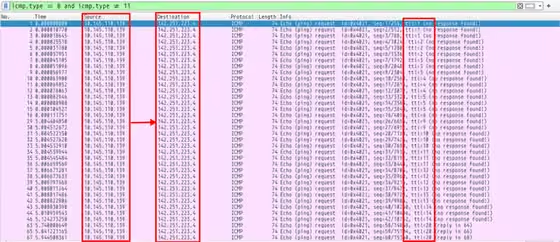
This helps us understand how traceroute and similar tools work. They send the destination many icmp echo requests with varying TTLs, and as these TTLs are decremented, they will all hit 0 at different routers, which will say TTL expired and send an ICMP packet back to the source (me)
Regarding fields that change, the Identification(ip header), TTLs, Sequence Numbers, and Checksums change between datagrams, and the others remain constant
- The Identification field of the IP Header increases starting at some base value and increases by one with each packet sent.
- The Identification for my first request packet is
0x437b
- The Identifier field of the ICMP Packet is some constant value for Echo Requests. The value is
0x4021 in my case (visible in the image)
- The Sequence Number field starts at 1 and increases by 1 for each request
The First ICMP Echo Reply
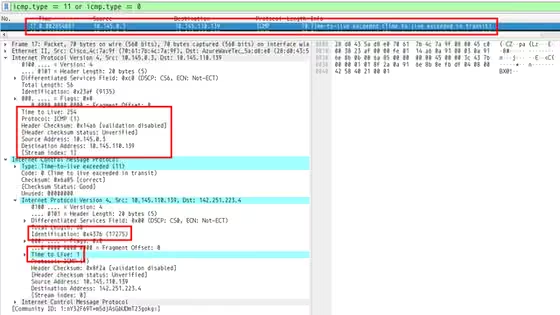
We see the first reply is from 10.145.0.3 which corresponds to our first entry in the traceroute
1 10.145.0.3 2.861 ms 2.848 ms 2.840 ms
You can see the IP Header of the request packet attached and its Identification field contains the value of the identifier of the ping whose TTL expired, which is the first packet, the one with the identification 0x437b mentioned above. The TTL field is set to 254. It was probably set to 255 (max possible) and decremented by one when the source (me) received it
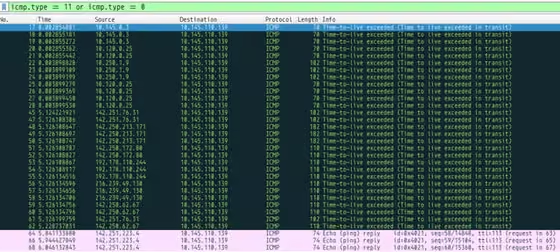
You can see the series of ICMP TTL exceeded replies sent by all the intermediate gateways that helped form our traceroute
2. Fetching a Webpage
captured packets with tshark while visiting http://gaia.cs.umass.edu/wireshark-labs/INTRO-wireshark-file1.html
Packet Capture Here
❯ tshark -i wlan0 -f "host 10.145.110.139" -w http.pcapng
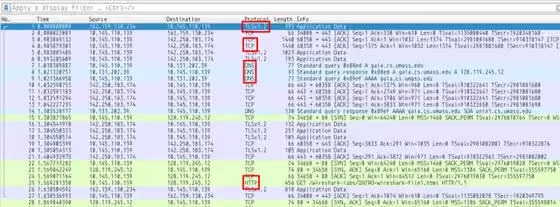
We see different protocols like TLSv1.2, TCP, DNS, and HTTP. We can analyse the different protocols in a .pcap with the Protocol Hierarchy too
Statistics -> Protocol Hierarchy
HTTP Protocol
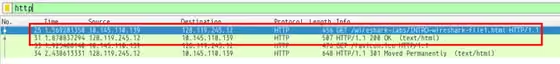
There was a latency of 301ms in fetching the site data
>>> 1.870837294 - 1.569281350
0.30155594399999996
Internet Address
When asked about the internet address of an address, we look at the IP Header of the packets involved. The IP Header looks like this
 0                   1                   2                   3
 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|Version|  IHL  |Type of Service|          Total Length         |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|         Identification        |Flags|      Fragment Offset    |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|  Time to Live |    Protocol   |         Header Checksum       |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                       Source Address                          |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                    Destination Address                        |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                    Options                    |    Padding    |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
Being a(the) network layer protocol its responsible for routing packets from the source address to the destination address. So looking at the IP Header of the HTTP GET request
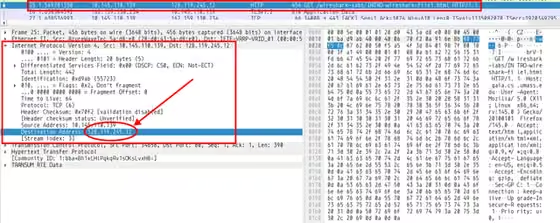
We can see the Internet Address is 128.119.245.12
By doing a DNS lookup we can try to identify the physical address of this IP
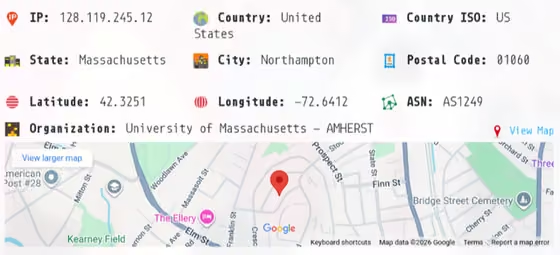
which as we can see maps to the University of Massachusetts
MAC Address
Medium Access Control address is also called the Ethernet address and is a unique ID given to every network hardware component. To find the MAC addresses in this HTTP packet we simply need to move a layer above the IP header and look at the Ethernet Header
Ethernet transmission layer (not necessarily accessible to the user):
    48.bit: Ethernet address of destination
    48.bit: Ethernet address of sender
    16.bit: Protocol type = ether_type$ADDRESS_RESOLUTION
Ethernet packet data:
    16.bit: (ar$hrd) Hardware address space (e.g., Ethernet, Packet Radio Net.)
    16.bit: (ar$pro) Protocol address space.  For Ethernet hardware, this is from the set of type fields ether_typ$<protocol>.
      8.bit: (ar$hln) byte length of each hardware address
      8.bit: (ar$pln) byte length of each protocol address
    16.bit: (ar$op)  opcode (ares_op$REQUEST | ares_op$REPLY)
    nbytes: (ar$sha) Hardware address of sender of this packet, n from the ar$hln field.
    mbytes: (ar$spa) Protocol address of sender of this packet, m from the ar$pln field.
    nbytes: (ar$tha) Hardware address of target of this packet (if known).
    mbytes: (ar$tpa) Protocol address of target.
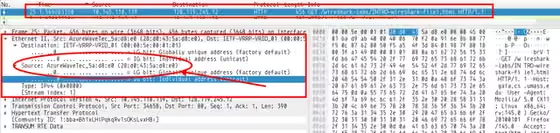
As we can see the MAC address of the source(me) is 28:d0:43:5a:d8:e0
We can verify this too
❯ cat /sys/class/net/wlan0/address
28:d0:43:5a:d8:e0

❯ ifconfig wlan0
wlan0: flags=4163<UP,BROADCAST,RUNNING,MULTICAST>  mtu 1500
        ether 28:d0:43:5a:d8:e0  txqueuelen 1000  (Ethernet)
MAC addresses can be used to identify the respective hardware vendors, turns out my Wifi module was made by AzureWave Tech.
06:00.0 Network controller: Realtek Semiconductor Co., Ltd. RTL8852BE PCIe 802.11ax Wireless Network Controller
however the actual chip used in the module was made by Realtek Semiconductor
TCP 3-Way Handshake
Transmission Control Protocol offers reliable, in-order, byte-stream services to applications. It's a transport layer protocol
 0                   1                   2                   3
 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|          Source Port          |       Destination Port        |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                        Sequence Number                        |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                    Acknowledgment Number                      |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|  Data |       |C|E|U|A|P|R|S|F|                               |
| Offset| Rsrvd |W|C|R|C|S|S|Y|I|            Window             |
|       |       |R|E|G|K|H|T|N|N|                               |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|           Checksum            |         Urgent Pointer        |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                           [Options]                           |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
|                                                               :
:                             Data                              :
:                                                               |
+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+
Most important are the Sequence Number and the Acknowledgement Number
From this helpful IBM article
- Sequence Number:
- TCP assigns a sequence number to every byte of data transferred
- The sequence number field tracks the sequence number of the byets transferred so far
- if a host has sent 1400 bytes so far, and is going to send a packet of size 200, the sequence number of the packet will be 1400 and after the packet is sent the sequence nunmber will be incremented to 1600
- Acknowledgement Number:
- this number is a counter to keep track of every byte received
- if 1000 bytes are received, it increases the acknowledgement number by 1000 when it sends out a packet in response
TCP is a connection-oriented protocol, it must establish a connection between two applications before sending packets. And HTTP is build on TCP so there must be packets establishing a connection with the website in the pcap. Wireshark very neatly separates these different TCP connections as streams for us
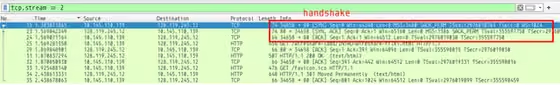
Lets look at the seq numbers and ack numbers (i am using the relative numbers provided by wireshark)
    SOURCE(ME)                                HOST(gaia.cs.umass.edu)

1.  SYN-SENT    --> <SEQ=000><ACK=000><CTL=SYN>      --> SYN-RECEIVED
2.  ESTABLISHED <-- <SEQ=000><ACK=001><CTL=SYN,ACK>  <-- SYN-RECEIVED
3.  ESTABLISHED --> <SEQ=001><ACK=001><CTL=ACK>      --> ESTABLISHED
It may be interesting to note that since the payload size of these packets is zero, there is no actual byte being consumed. Instead the protocol specifies that since the SYN flag is set the ACK will send client seq + 1. This is our "ghost byte". So if we received a pure ACK without the SYN flag (like the 3rd packet of the handshake) it doesn't increase either the seq_num or ack_num since there's no actual data
We can also look at the GET request and the acknowledgement sent by the server. Note the GET had a TCP payload of 390 bytes
    SOURCE(ME)                                       HOST(gaia.cs.umass.edu)

4.  GET-REQST   --> <SEQ=001><ACK=001><CTL=PSH,ACK>  --> GET-REQ-RECV
5.  SUCCESSS    <-- <SEQ=001><ACK=391><CTL=ACK>      <-- GET-REQ-RECV (ACK)
The server has successfully acknowledged the 390 bytes we sent it
DNS Queries
Every DNS packet has the below basic format. An RR is a Resource Record
+---------------------+
|        Header       |
+---------------------+
|       Question      | the question for the name server
+---------------------+
|        Answer       | RRs answering the question
+---------------------+
|      Authority      | RRs pointing toward an authority
+---------------------+
|      Additional     | RRs holding additional information
+---------------------+
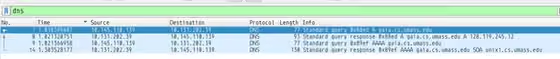
The queries went to the first DNS recursor where it found an entry because it must have been cached and the recursor returned two records
- A record: standard ipv4 address record
- AAAA record: returns ipv6 record
I don't see any CNAME records for this address
The response times were 2ms for the A record and 282ms for the AAAA record
>>> 1.021320751 - 1.018389887
0.0029308639999998665
>>> 1.303528177 - 1.021366958
0.282161219
HTTPS vs HTTP
Packet capture here
Browsers these days usually upgrade the HTTP connection to an HTTPS one. HTTPS includes a seecurity layer that encrypts HTTP traffic.
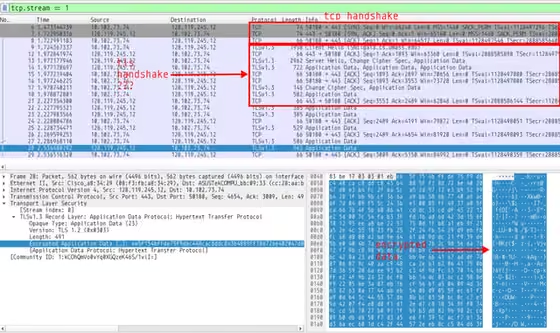
I don't know the internals of TLSv1.3 enough to properly recognise where the handshake ends, but as we can see key exchanges and random secrets and certificates are being exchanged in there somewhere
This results in our final payloads being encrypted and unreadable to an interfering body (also me). You may also note that HTTPS traffic goes to port 443 on the server instead of port 80 like in HTTP
Course Website here.
- contains slides and many papers/rfcs
Textbook here
linked from